
 Critical PHP flaws: update PHP on your WordPress site now Two critical PHP flaws disclosed on 21 October 2026 (CVE-2026-109618 and CVE-2026-109619) let an attacker run code on a server without logging in. Update to PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12. Here is how to check, how to update, and what to do if you can't yet.
 AI agent identity: knowing which agent is calling, and why that is only half the problem Agent identity is becoming solvable: signed requests, published key directories, authorisation mandates. A verified agent can still buy all your inventory, so identity is the foundation and not the answer. ChatGPT Atlas has been discontinued: what replaced it and what it means for your site OpenAI switched Atlas off on 9 August 2026, 292 days after launch. The browser is gone, the agentic traffic is not, and the replacements reach your site from different places.
 Perplexity Comet: what an agentic browser does to your site, and the court case about it Comet is free on every platform and its agent acts on sites for a real user. Amazon sued over exactly that, won an injunction, then lost it on appeal. The access question is now a live legal one.
 MCP security: the five ways agent tool access goes wrong MCP turns tool descriptions into model context, which makes the integration layer an attack surface. Tool poisoning, confused deputy, token passthrough, SSRF and rogue servers are the five that matter. x402 and agent payments: what a machine-payable endpoint means for your site x402 revives HTTP 402 so an agent can pay for a request in stablecoins and retry it. That turns abuse into a priced transaction, and it does not decide who is allowed to buy. llms.txt: we publish one, and no AI crawler has ever read it We have published an llms.txt since May 2026. Across four days of IP-verified logs, AI crawlers fetched our robots.txt 120 times and our sitemap 43 times. They fetched llms.txt zero times. Agentic browsers: your customer is now a robot, and that is fine An agentic browser is automation operated by a real customer. It fails every classic bot test and still deserves to reach your checkout. The answer is to require evidence of a human on particular steps, rather than to judge the client. OWASP API Security Top 10: which two a bot layer actually fixes Eight of the ten risks in the 2023 OWASP API Security Top 10 are authorization and inventory bugs only your own code can fix. API4 and API6 are the two where a bot-protection layer is the right tool.
 Why Do Bots Fill Out Forms? The Economics of Form Spam and How to Stop It Why do bots fill out forms? For free advertising, credential stuffing, signup-credit abuse, SEO laundering through expired domains, and reconnaissance. Here is how each one works, and how Prosopo blocks them at the form-submission layer.
 What is WAAP? Web Application and API Protection explained WAAP means Web Application and API Protection: a WAF, DDoS mitigation, bot management and API protection sold as one cloud service. The bot component is the one to scrutinise, because it needs signals a network vendor has no reason to collect.
 Gartner and bot management: the Magic Quadrant that does not exist There is no Gartner Magic Quadrant for bot management. There is one for Cloud WAAP, and bot mitigation is a criterion inside it. Where each vendor appears, and how to read the two analyst views together. OWASP automated threats: the 21 names your vendor should be using The OWASP Automated Threat Handbook gives every bot attack a vendor-neutral name and an OAT number. The full taxonomy, the five that cost the most money, and how to use it in an RFP. Web Bot Auth: signed agents solve identity, not intent Web Bot Auth lets an AI agent cryptographically sign its requests so you can verify who it is. That fixes user-agent spoofing and leaves the harder question untouched: a verified agent can still be doing something you do not want. CAPTCHA · PoW CAPTCHA Explained: What It Is, and Why It Isn't Enough on Its Own Proof-of-work CAPTCHA explained — how the hash-puzzle mechanism works, why it went mainstream after reCAPTCHA's price hike, and what it still can't stop on its own.
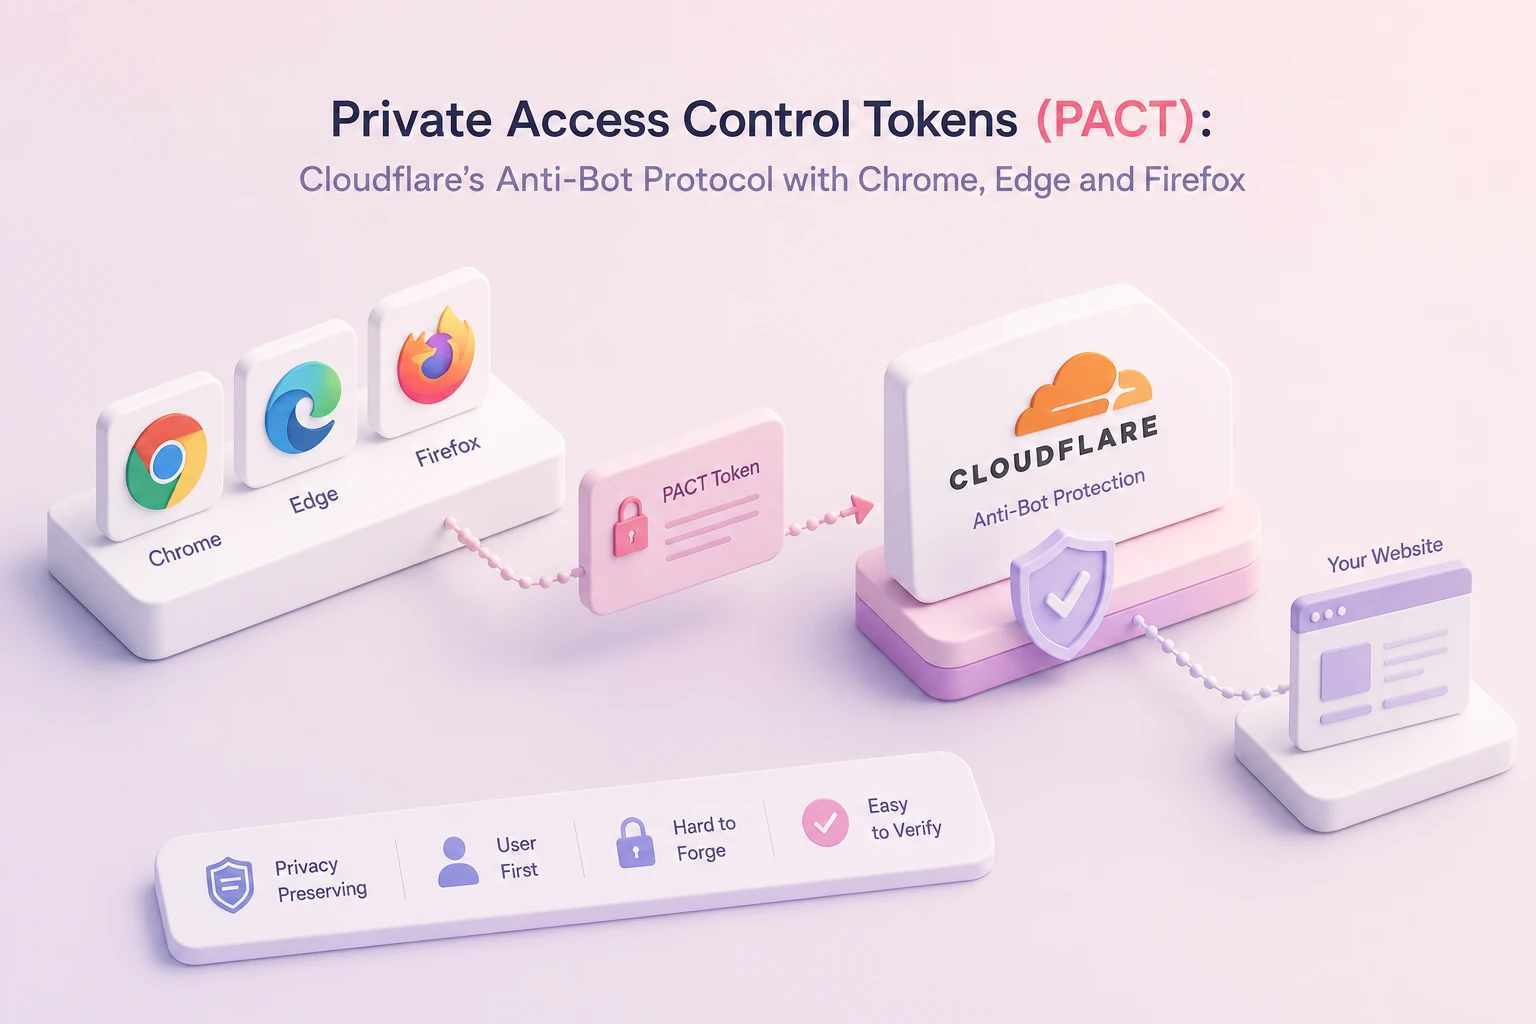 Private Access Control Tokens (PACT): the Privacy Pass successor from Cloudflare, Chrome, Edge and Firefox Cloudflare, Chrome, Edge, Firefox and Shopify announced Private Access Control Tokens (PACT) on 22 June 2026. It is the first descendant of Privacy Pass with more than one browser behind it. Private Access Tokens was only ever released in Safari, and Private State Tokens never got multi-vendor support.
 Top Arkose Labs Alternatives 2026: Enterprise Bot Defense Without the Game Challenge Best Arkose Labs alternatives for 2026 — compare DataDome, HUMAN, Kasada and Prosopo for enterprise bot defense without visible game challenges.
 Top DataDome Alternatives 2026: Enterprise Bot Defense Compared Best DataDome alternatives for 2026 — compare HUMAN, Kasada, Arkose Labs, Cloudflare and Prosopo on price, coverage and EU data residency.
 CAPTCHA · Top hCaptcha Alternatives 2026: Invisible, Private, No Image Puzzles Best hCaptcha alternatives for 2026 — compare Procaptcha, Cloudflare Turnstile, reCAPTCHA v3 and Friendly Captcha on pricing, privacy and bot detection. CAPTCHA · hCaptcha vs Cloudflare Turnstile 2026: Which Wins (and When Neither Does) hCaptcha vs Cloudflare Turnstile in 2026 — pricing, catch rate and privacy compared. Turnstile is free but pass-only, hCaptcha stricter but paid.
 CAPTCHA · reCAPTCHA vs Cloudflare Turnstile 2026: Which One (and When Procaptcha Beats Both) reCAPTCHA vs Cloudflare Turnstile in 2026 — pricing, catch rate and privacy compared. reCAPTCHA gives a score, Turnstile is free, both are US processors. CAPTCHA · reCAPTCHA vs hCaptcha 2026: Which One (and Why Procaptcha Often Wins Both) reCAPTCHA vs hCaptcha in 2026 — pricing, GDPR, catch rate compared. reCAPTCHA is cheaper at low volume, hCaptcha stricter, both are US data processors.
 Ticketing · How to Stop Ticket Scalping: The 2026 Anti-Bot Playbook How to stop scalpers and stop scalping in 2026 — block scalper bots, residential proxies and bulk signups at the queue, ticket page, drop API and CDN edge. CAPTCHA · Forrester Wave Bot and Agent Trust Management Q2 2026: How Prosopo Compares Forrester's Q2 2026 Wave named 8 Bot and Agent Trust Management vendors. What each got dinged for, and how Prosopo — the specialist entry — compares. CAPTCHA · How to Stop PHP Form Spam (Without a Plugin) If your PHP mail script is being abused by bots, stop the bot before mail() runs — server-side CAPTCHA verification in a few lines of PHP, via Procaptcha.
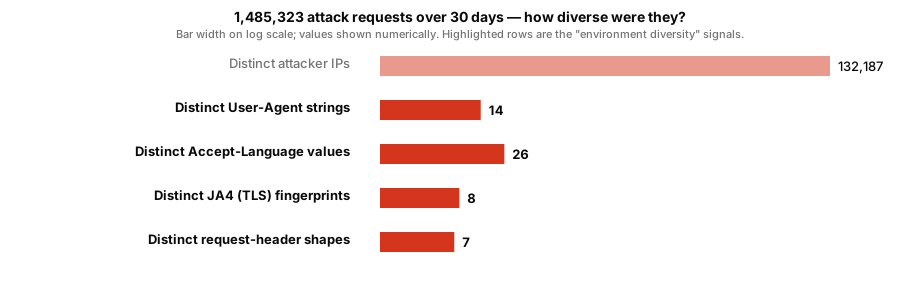 Technical · Faking browsers is easy — but not at scale 131,819 residential US IPs threw 1.4M brute-force attempts at one mobile-only customer in 30 days — all collapsing onto a handful of fingerprints.
 Privacy · Google reCAPTCHA Switches to Data Processor - Too Little, Too Late? Google flips reCAPTCHA to data processor in April 2026 — after a decade of harvesting visitor data. Why the switch, and why it doesn't fix GDPR risk.
 Technical · How to Add CAPTCHA to Fastly CDN Learn how to integrate Procaptcha with Fastly CDN to protect your website from bot attacks while maintaining performance and user privacy.
 CAPTCHA · We cut our Mongo DB costs by 90% by moving to Hetzner We moved MongoDB Atlas off AWS and onto self-hosted Hetzner boxes — 90% cost cut, no performance loss. Here's the setup, the Ansible, and what broke.
 CAPTCHA · reCAPTCHA is Changing Its Terms of Service — What Site Owners Need to Do Google's reCAPTCHA is showing 'Take action' on sites with older keys. What the ToS change means, which keys are affected, and how to remediate. Ticketing · 🎫 Preventing Ticket Bots - The Battle for Fair Access Ticket bots continue to plague the live event industry in 2026, frustrating fans and inflating prices. Discover the latest strategies to prevent them.
 CAPTCHA · How to Choose a GDPR-Friendly CAPTCHA for WordPress Stop spam & stay GDPR-compliant! Learn how to choose a GDPR-friendly CAPTCHA for WordPress that boosts security without tracking.
 CAPTCHA · How to Integrate CAPTCHA Without Violating User Rights Integrate CAPTCHA the right way! Ensure security, privacy, and accessibility without violating user rights. Follow our expert guide for best practices!
 Ticketing · Why is Ticket Scalping so Hard to Stop? Uncovered Uncover the dark secrets of ticket scalping, from bots to black markets. See why it's so hard to stop and what can be done. Don't miss out - read now!
 CAPTCHA · How to Test Your Ansible Playbooks Locally Testing your Ansible playbooks locally can save you time and effort. Here are some tips to help you get started.
 Company · We Are Being Blackmailed or: How Not to Hire a Contractor A contractor that we hired on Upwork is now blackmailing us. Here's how we got into this situation and how we're dealing with it.
 CAPTCHA · tsx vs ts-node: Time to Drop ts-node for tsx tsx vs ts-node compared: why tsx runs TypeScript faster than ts-node, and how to migrate your Node.js scripts away from ts-node today. Technical · Using Vite To Rebuild Local Dependencies in an NPM Workspace Vite ignores local workspace packages because they sit outside its module graph — the config trick that forces Vite to rebuild sibling npm packages.
 CAPTCHA · What is the best value CAPTCHA in 2024? Find out what the best value CAPTCHA is in 2024 and how it compares to other popular CAPTCHA solutions.
 CAPTCHA · Switching From reCAPTCHA to Prosopo: What's Involved What changes when you swap reCAPTCHA for Prosopo — integration surface, verdict shape, GDPR posture, and what your team sees in the dashboard.
 CAPTCHA · Invisible Captcha: A Silent Solution by Prosopo Invisible captcha blocks spam and abuse without a challenge screen — how Procaptcha runs silently in the background and only interrupts suspicious traffic.
 CAPTCHA · Stop giving your website data away! Find out why reCAPTCHA, hCaptcha, and Cloudflare Turnstile may be secretly monetising your website data, and how Prosopo's Procaptcha is solving this problem. Technical · How to deploy Procaptcha on your website or app How to switch from Google's reCAPTCHA to Prosopo Procaptcha and protect your website or app from bots for free.
 Company · Prosopo team at Polkadot Decoded 2022 Prosopo at Polkadot Decoded 2022 in Berlin — Gavin Wood on Governance v2, Encointer on UBI, and why web3 still needs bot protection at the wallet layer. Company · Prosopo receives grant from Web3 Foundation to build human verification Prosopo has received a Web3 Foundation grant to build a decentralised human verification marketplace, developed with Gimly to protect DApps from bot attacks.
See what's reaching your site
A Bot Exposure Assessment is a 30-minute call with an engineer. We look at your traffic, show where your current setup leaves gaps, and agree how a trial would be judged. Nothing to install first.