
SMS pumping fraud: what it is and how to stop it
SMS pumping is bots requesting OTP texts to number ranges a rogue carrier shares revenue on, and you pay for every one. How to spot it and stop it.
7 min read
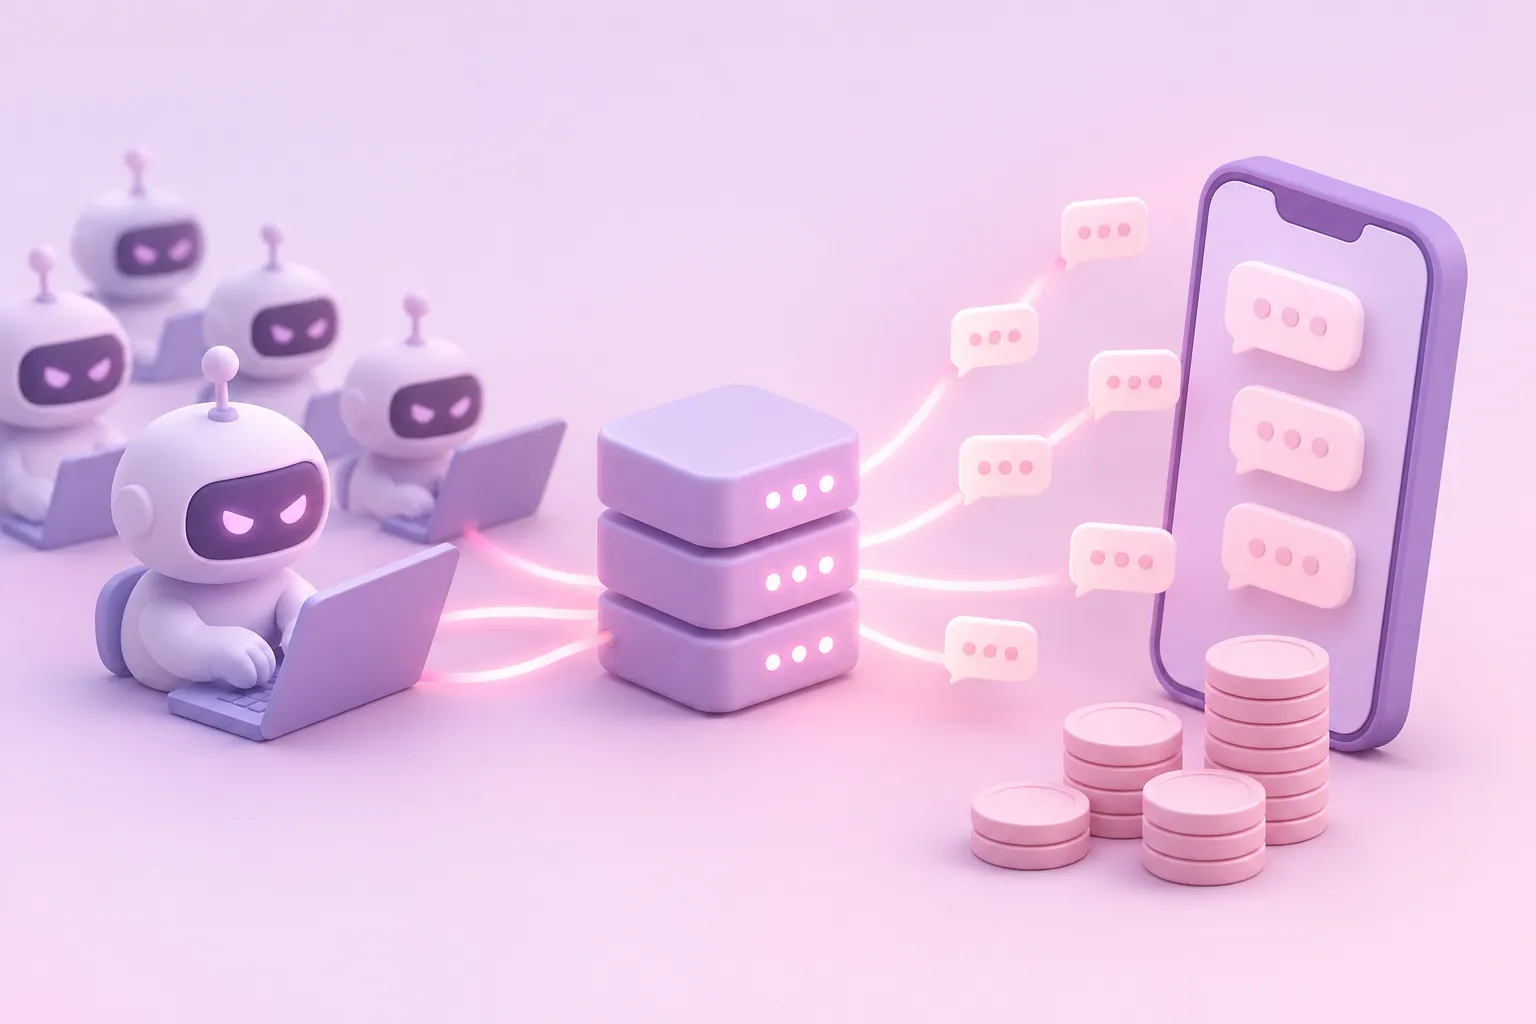
SMS pumping is a fraud in which bots use a form on your site or app to send text messages, usually one-time passcodes, to phone numbers the fraudster earns money from. Nobody is trying to log in or sign up. The aim is the SMS bill, which you pay and they take a share of.
It goes by several names. Developers tend to say SMS pumping or SMS toll fraud. Messaging providers call it artificially inflated traffic, or AIT: Vonage describes AIT as "a type of SMS fraud" in which bots and scripts flood SMS channels with fake messages, and Sinch as fraud "carried out by fraudsters who generate high volumes of fake traffic".
How SMS pumping works
Twilio's guide to preventing fraud in Verify puts it simply: fraudsters "take advantage of a phone number input field to receive a one-time passcode", the messages go to a range of numbers controlled by one mobile network operator, and the fraudsters "get a share of the generated revenue" while you pay for the traffic.
Sinch sets out the usual sequence:
- A fraudster builds a bot that creates fake accounts or fills in a form that sends an SMS.
- The bot triggers a one-time passcode to each mobile number on its list.
- A rogue party in the delivery chain receives the traffic without delivering it to real people.
- They split the revenue, and repeat.
The numbers are often in countries where a text costs more to deliver, which leaves a bigger fee to share. No code is ever entered, because nobody is reading the messages.
Who gets hit by SMS pumping
Any form or API endpoint that sends a text in response to a phone number someone typed in is exposed. That includes:
- signup forms that verify the phone number
- login with a one-time code, and SMS two-factor authentication
- password reset and account recovery by SMS
- "text me a link to the app" and "send me a quote" forms
- chatbots that reply by SMS
The best-known claim of the cost comes from Twitter. On 18 February 2023, Elon Musk posted that "Twitter is getting scammed by phone companies for $60M/year of fake 2FA SMS messages". CNN reported the same day that Twitter would limit SMS two-factor authentication to paying Twitter Blue subscribers from 20 March 2023. The $60 million is Musk's own figure and was never published in audited accounts, but it shows the kind of sum a large sender can lose.
How to spot SMS pumping
Twilio's SMS pumping guide and its Verify documentation list the same handful of signs:
- A spike in SMS volume or spend that does not match a rise in signups or logins.
- Unusual country codes. Texts going to countries where you have few or no customers.
- Sequential or clustered numbers. Runs of numbers with the same prefix, such as ending 1000, 1001, 1002.
- A falling OTP conversion rate. The share of sent codes that are then entered drops, especially for one country.
- Requests from Tor, proxies, VPNs or cloud providers, and request patterns that look scripted.
The conversion rate is the hardest sign for an attacker to hide, because a pumping bot never enters the codes it triggers.
SMS pumping defences
Turn off SMS to countries you do not serve. Twilio calls these geographic permissions. If you only sell in the UK and Ireland, there is no reason for your signup form to text a number elsewhere, and tighter limits can apply to higher-risk countries you do serve.
Rate-limit sends, per phone number, per number range, per IP, per device and per session, and add a growing delay before a code can be resent to the same number. Twilio notes that rate limits "may not prevent fraud but can slow the attackers down", because a bot using many numbers and many proxies stays under each individual limit.
Require evidence of a human before sending any SMS. Every text in a pumping attack is triggered by an automated request, so a check on the form or API call that sends the text removes the attack at its source rather than limiting it. Twilio's own guidance recommends bot detection or a CAPTCHA on these flows. Put the check before the send, not after the code is entered.
Turn on your SMS provider's fraud guard. Twilio Verify Fraud Guard blocks destination prefixes when it sees unusual traffic, and Vonage's AIT Protection blocks or alerts on suspicious traffic at a level you choose. Both work on the destination numbers after a request has reached your provider, so they complement a check on who is making the request.
Send SMS only to mobile numbers. Twilio suggests a carrier lookup to check the line type first, so landlines and other non-mobile numbers are never sent a code.
Alert on the OTP conversion rate. A drop in codes entered against codes sent, broken down by country, catches a slow attack that keeps total volume flat.
How Prosopo stops SMS pumping
Procaptcha adds a check to the form that sends the text, so a bot has to pass it before your backend asks your SMS provider to send anything. Real visitors pass invisibly in most cases, and a suspected bot gets a proof-of-work or image challenge or is blocked. If you need to, Procaptcha's Traffic Filter can also block requests from Tor, VPN and proxy networks per site, which are among the signs Twilio lists.
Where the SMS is sent from an API that mobile apps or other clients call directly, Prosopo Protect checks every request at your edge on Cloudflare Workers or AWS Lambda@Edge, and its Access Rules can block or challenge by country, ASN, IP range and TLS fingerprint before the request reaches your code.
For bot-driven signups more broadly, see spam bot protection.
SMS bill jumped for no reason?
A Bot Exposure Assessment is a 30-minute call with an engineer. We look at your traffic, show where your current setup leaves gaps, and agree how a trial would be judged. Nothing to install first.
Questions
Something else? Ask an engineer.
What is SMS pumping?
SMS pumping is a fraud in which bots enter phone numbers into a form that sends a text, usually a one-time passcode for signup, login or password reset, so that your business pays to send thousands of messages to numbers the fraudster has arranged to earn from. Twilio describes it as fraudsters taking advantage of a phone number input field to receive a one-time passcode, with the fraudsters getting a share of the revenue the traffic generates.
What is SMS pumping fraud also called?
It is also called SMS toll fraud, SMS traffic pumping, and artificially inflated traffic or artificial inflation of traffic, both shortened to AIT. AIT is the term used by messaging providers such as Sinch and Vonage.
How do fraudsters make money from SMS pumping?
Sending a text to a mobile number costs the sender a fee, part of which goes to the network that delivers it. The fraudster works with a rogue party in that chain, often a carrier or intermediary controlling a range of numbers, which receives the traffic without delivering it to real people, and the two split the fees. Your business pays the bill.
How do I know if I am being hit by SMS pumping?
The common signs are a sudden rise in SMS spend or volume, texts going to country codes where you have few customers, numbers in a run with the same prefix such as ending 1000, 1001, 1002, and a falling OTP conversion rate, meaning far fewer codes are entered than are sent.
How do you stop SMS pumping?
Turn off SMS to countries you do not serve, rate-limit sends per number, number range, IP, device and session, add a delay before resending a code, require evidence of a human before the form sends any text, turn on your SMS provider's fraud guard, and alert when the OTP conversion rate drops. Requiring evidence of a human removes the bot that drives the attack; the other steps limit the damage from whatever still gets through.
Did Twitter really lose $60 million to SMS pumping?
That figure comes from Elon Musk, not from audited accounts. On 18 February 2023 he posted that Twitter was 'getting scammed by phone companies for $60M/year of fake 2FA SMS messages', around the time Twitter announced that SMS two-factor authentication would only be available to paying Twitter Blue subscribers from 20 March 2023.
Related reading
 CAPTCHA · How to Stop PHP Form Spam (Without a Plugin) If your PHP mail script is being abused by bots, stop the bot before mail() runs — server-side CAPTCHA verification in a few lines of PHP, via Procaptcha.
 Why Do Bots Fill Out Forms? The Economics of Form Spam and How to Stop It Why do bots fill out forms? For free advertising, credential stuffing, signup-credit abuse, SEO laundering through expired domains, and reconnaissance. Here is how each one works, and how Prosopo blocks them at the form-submission layer.
 CAPTCHA · Procaptcha vs Friendly Captcha - Why Real Bot Protection Matters in 2026 Procaptcha vs Friendly Captcha in 2026 — catch rate, GDPR posture and pricing compared. Friendly is proof-of-work only; Procaptcha catches real bots.
 Technical · How to Add CAPTCHA to Fastly CDN Learn how to integrate Procaptcha with Fastly CDN to protect your website from bot attacks while maintaining performance and user privacy.
 CAPTCHA · Cloudflare Turnstile Alternatives 2026 — 8 Options Ranked Turnstile returns a pass/fail token and nothing to escalate to. How Prosopo, hCaptcha, ALTCHA and 5 others compare on catch rate, GDPR and price.
 Top Arkose Labs Alternatives 2026: Enterprise Bot Defense Without the Game Challenge Best Arkose Labs alternatives for 2026 — compare DataDome, HUMAN, Kasada and Prosopo for enterprise bot defense without visible game challenges.